Email currently traversing the internet with an M$ Word attachment asking the recipient to "please open". Would your users respond properly?
Per this Websense File Sandbox report, the file is clearly malicious. Unfortunately, the "Premium AV Guys (McAfee & Symantec)" are asleep at the wheel again:
As such, you likely want to check your firewall logs to see if your users did indeed open the attachment/dropper and are therefore phoning home to the following IP Addresses:
Thursday, October 1, 2015
Thursday, September 24, 2015
Blended Threats/Controls
Question - considering the plethora of Blended Threats which leverage both the Email & Web channels to exploit our networks... is it important that our Security Controls have visibility into both mediums?
Case in point - current phishing email traversing the internet which leverages legitimate looking graphics (directly below). Wouldn't it be nice if your web security solution knew of these spam/phishing URLs? On the flip side, wouldn't it be nice if your email security solution knew about malicious URLs?
As you'd expect, the link redirects to a malicious site... located in the Netherlands in this instance. Question - how important is it that your security solutions have a worldwide research team/presence?
Note that the site is attempting to obfuscate the content by leveraging javascript and Base64 encoding:
Final question - wouldn't it be nice if your security solutions not only had a worldwide presence in the Web & Email channels... but could also block active code (javascript, java, active-x) ala the Websense ACE Engine? :-)
Case in point - current phishing email traversing the internet which leverages legitimate looking graphics (directly below). Wouldn't it be nice if your web security solution knew of these spam/phishing URLs? On the flip side, wouldn't it be nice if your email security solution knew about malicious URLs?
As you'd expect, the link redirects to a malicious site... located in the Netherlands in this instance. Question - how important is it that your security solutions have a worldwide research team/presence?
Note that the site is attempting to obfuscate the content by leveraging javascript and Base64 encoding:
Final question - wouldn't it be nice if your security solutions not only had a worldwide presence in the Web & Email channels... but could also block active code (javascript, java, active-x) ala the Websense ACE Engine? :-)
Tuesday, September 15, 2015
Malvertising Campaign
Dark Reading is running a story regarding a 3 week malware campaign in which Online Ad Networks enabled miscreants to redirect clicks to sites hosting the Angler Exploit Kit. The full story can be found here.
Note that the Security Community in general considers this a "big security blunder". However, of special note, is the following quote:
"A fraudulent ad server using HTTPS. We were basically blind to it," he says.
Question - are you still putting off HTTPS Decryption? Wouldn't it be nice if you had Security Controls with visibility into your encrypted traffic and that ongoing attack??
Response - Yes, HTTPS Decryption and proxies in general can be complex... but ESPO Systems can help you with our Best Practices. :-) An additional advantage to consider, as identified within another story running on Dark Reading regarding questionable CAs, found here, is easily addressed when you have a Websense Proxy and thereby have a central location to control CAs:
Note that the Security Community in general considers this a "big security blunder". However, of special note, is the following quote:
"A fraudulent ad server using HTTPS. We were basically blind to it," he says.
Question - are you still putting off HTTPS Decryption? Wouldn't it be nice if you had Security Controls with visibility into your encrypted traffic and that ongoing attack??
Response - Yes, HTTPS Decryption and proxies in general can be complex... but ESPO Systems can help you with our Best Practices. :-) An additional advantage to consider, as identified within another story running on Dark Reading regarding questionable CAs, found here, is easily addressed when you have a Websense Proxy and thereby have a central location to control CAs:
Tuesday, September 1, 2015
Cisco = Security?
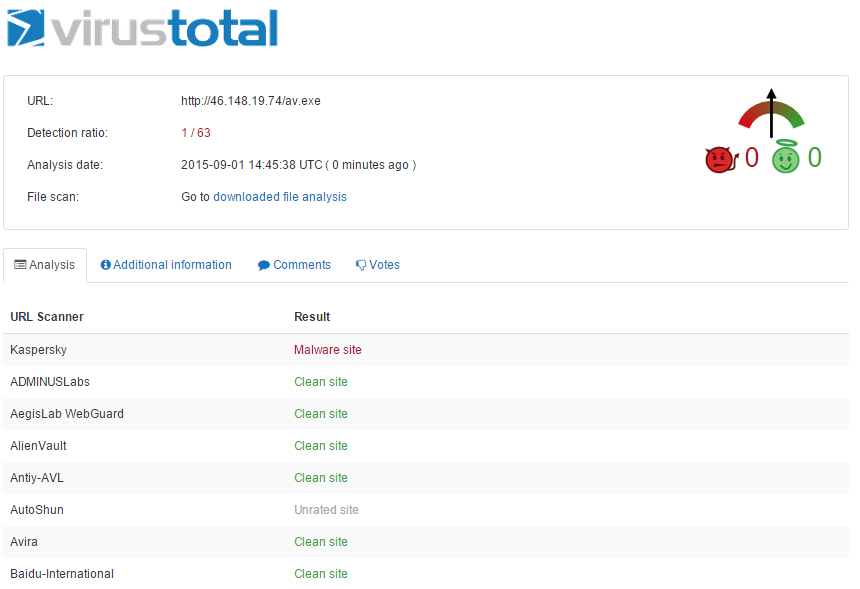
An attack is currently underway in which a dropper file downloads additional malware from the following site:
Per the VirusTotal screenshot below, only 1 of 63 vendors is blocking... other than Websense:
If you've bought into the Cisco dogma of a unified/secure network, you're likely hoping your IronPort Web Proxy with associated SenderBase Reputation System will protect you. Ummmmm... no:
Per the VirusTotal screenshot below, only 1 of 63 vendors is blocking... other than Websense:
If you've bought into the Cisco dogma of a unified/secure network, you're likely hoping your IronPort Web Proxy with associated SenderBase Reputation System will protect you. Ummmmm... no:
Tuesday, August 25, 2015
Another day...
...another attack in which the "Premium" Security Guys (McAfee & Symantec) are AWOL:
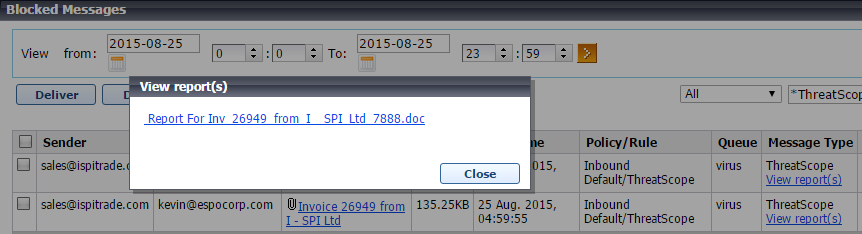
- Email traversing the internet this morning with a subject of "Invoice 26949 from I SPI Ltd". The M$ Word attachment is named Report For Inv_26949_from_I__SPI_Ltd_7888.doc
- Per this Websense File Sandbox Report, the malware modifies 23 Files, 2 Processes and 417 Registry Settings. However, the "Premium" Security/AV Guys currently find no problem with the file:
- Additionally, per the above Websense File Sandbox report, you'll notice that the malware also phones home to a site in Poland to download an additional exe. You may therefore ask, "can the "Premium" Security Guys at least protect me from this portion of the blended threat?" Ummm... no:
- Email traversing the internet this morning with a subject of "Invoice 26949 from I SPI Ltd". The M$ Word attachment is named Report For Inv_26949_from_I__SPI_Ltd_7888.doc
- Per this Websense File Sandbox Report, the malware modifies 23 Files, 2 Processes and 417 Registry Settings. However, the "Premium" Security/AV Guys currently find no problem with the file:
- Additionally, per the above Websense File Sandbox report, you'll notice that the malware also phones home to a site in Poland to download an additional exe. You may therefore ask, "can the "Premium" Security Guys at least protect me from this portion of the blended threat?" Ummm... no:
Friday, August 14, 2015
McAfee & Symantec... asleep at the wheel
Remind me again how we block malicious macros in Microsoft Files. Attachment blocking? Nope... not if it's a MS Office file. Antispam signatures? Kinda... but not 100% effective. Antivirus? Well... that's what we've put our trust in for the last decade. Good decision? Consider the following:
- Email traversing the internet this morning with a subject of "invoice" and an attached excel file:
- Per this Websense File Sandbox Report, the file modifies 53 Registry Settings and downloads an executable from a recently compromised site. In fact, the download is from a valid government site for the City of Noale Italy that has recently been compromised. Quick Question/Test - would your web filtering solution block that HTTP connection? :-)
- Lastly, and as is so often the case, the vendors who command such a premium for reactive signature-based AV solutions (McAfee and Symantec) are again MIA. Would it, therefore, make sense to reduce your AV budget by purchasing one of the vendors referenced below, and then reapply those savings towards an advanced security solution?
- Email traversing the internet this morning with a subject of "invoice" and an attached excel file:
- Per this Websense File Sandbox Report, the file modifies 53 Registry Settings and downloads an executable from a recently compromised site. In fact, the download is from a valid government site for the City of Noale Italy that has recently been compromised. Quick Question/Test - would your web filtering solution block that HTTP connection? :-)
- Lastly, and as is so often the case, the vendors who command such a premium for reactive signature-based AV solutions (McAfee and Symantec) are again MIA. Would it, therefore, make sense to reduce your AV budget by purchasing one of the vendors referenced below, and then reapply those savings towards an advanced security solution?
Thursday, August 6, 2015
Symantec Focused on Split?
As Symantec finally realizes that Security + Storage does not equal a valid business model and thereby prepares for their upcoming split, we at ESPO ask a question - is Symantec focused on Wall Street or your security? Consider the following:
- An ~80KB M$ Word doc with malicious macro is traversing the Internet today with a subject line of "Debit". The Websense File Sandbox report can be found here. Note how the malware performs a Zeus-like HTTP POST to a malware site in Germany.
- Convinced it's a bad file that you wouldn't want your Finance Dept receiving? Convinced that your Symantec AV has you covered?? May want to think again regarding that second question:
In closing, it's a nice to see McAfee catching this latest variant as we've beaten up on them recently. However, we still strongly advise clients put a File Sandboxing solution in place ASAP.
- An ~80KB M$ Word doc with malicious macro is traversing the Internet today with a subject line of "Debit". The Websense File Sandbox report can be found here. Note how the malware performs a Zeus-like HTTP POST to a malware site in Germany.
- Convinced it's a bad file that you wouldn't want your Finance Dept receiving? Convinced that your Symantec AV has you covered?? May want to think again regarding that second question:
In closing, it's a nice to see McAfee catching this latest variant as we've beaten up on them recently. However, we still strongly advise clients put a File Sandboxing solution in place ASAP.
Subscribe to:
Posts (Atom)