Yes... we agree that Barracuda is "cost effective". You too could create cost effective solutions if you leveraged open source tools. However, the question needs to be asked, are you willing to reduce your risk posture to save a few bucks? Case in point:
M$ Word file started propagating across the Internet with malicious macros at ~7:45amCST. This file is actually a Dropper File, as shown via this Forcepoint File Sandbox Report, which is attempting to infect your local files and phone home to a website in the US:
What is the Anti-Virus Coverage Rate you may ask for this Dropper File? Not good... only 5 companies currently detect it:
OK... lets assume your security controls have not blocked the download of the dropper, is your Barracuda Solution going to protect you from the download of the actual payload? Ummm... no:
In summary, please contact ESPO Systems if you'd like to implement controls to block the attack across the entire Kill Chain.
Thursday, January 28, 2016
Wednesday, January 13, 2016
Symantec + Cisco = Bad Day
Do you have Symantec's AV + Cisco's Web Gateway? If so, you may be in for a bad day. Why? Malware is currently working it's way around the Internet that neither vendor is protecting against:
Per this Raytheon|Websense File Sandbox Report, a malicious Word Document is being propagated that is actually a Dropper File for Dridex. If you are hoping Symantec will protect your IT Assets against this threat... you will be disappointed:
Next, assuming the Dropper File was not detected, it's now downloading additional malware from a website on the GoDaddy domain:
If you are hoping your Cisco / IronPort Web Gateway is protecting your IT Assets... you will be disappointed again:
In summary, your security solution needs to be holistic... you need to have visibility into all 7 steps of the Kill Chain. Call ESPO Systems for a free consultation.
Tuesday, December 15, 2015
Cryptolocker being installed via HTTPS
We know, we know, we know... proxies are complex. It's much easier to install a Next Gen Firewall and check the box. However, what are you going to do about DLP? Additionally, what are you going to do about the latest Cryptolocker attack? Per here and below, Firefoxpatch.exe, which is indeed malware, is being distributed via the phaaccounty-taxes website:
Your answer may be to turn on HTTPS Decryption. We'll let you in on an ugly little secret... most Next Gen Firewalls have performance degradation issues when this feature is turned on per this NSS Labs Test:
Are we saying Next Gen Firewalls are not the answer? Not at all... they are absolutely part of the answer as the IPS, VPN, Application ID capabilities and traditional firewalling features are necessary. However, you need to augment these solutions with feature rich proxies ala the Raytheon|Websense APX Solution to enable a complete Security Architecture. Schedule a briefing with ESPO Systems today to learn more.
Thursday, December 10, 2015
Dridex Operational This Morning
A Microsoft Word document, currently named Order Acknowledgement.doc, is propagating across the Internet this morning. Per below, the doc has a malicious macro and is being leveraged as a dropper:
As we've seen all too frequently, the dropper will not only ping the Botnet via high numbered TCP Ports (TCP:3448 today)... but will also pull another exe into the environment:
As stated previously, the FBI was a little too aggressive with it's "marketing" of the takedown of Dridex in mid-October... as this is the same malware variant. And, as has been seen frequently over the last year, our AV Vendors are not keeping up with these initial volleys with only 6 of 55 companies currently detecting:
In summary, the Raytheon|Websense APX Solution is one of the few vendors capable of protecting against this threat... across the entire Kill Chain. Contact ESPO Systems if you'd like to schedule a briefing.
Monday, November 30, 2015
Black Monday
Yes... we know the labels are Black Friday and Cyber Monday. However, a Microsoft Word document with malicious macro is propagating across the Internet this morning (Raytheon|Websense File Sandbox Report here) with only 1 of 54 AntiVirus Engines protecting... hence Black Monday:
Question - with such a poor detection rate by the AV Engines, and, our inability to outright block all incoming Microsoft Files (as our User Communities would scream)... what are you to do? Assuming you're not already protecting yourself with a Raytheon|Websense APX Solution, you may need to scour your firewall logs for the phone home back to the botnet on TCP Port 2448 :-(
Monday, November 23, 2015
Blended Failure
What is a Blended Threat? Per TechTarget, it's one that usually employs multiple attack vectors. In other words, the threat usually comes in via the email threat vector, but, a dropper file typically phones home to pull additional malware via the web threat vector. Today we have an example of the Security Vendors missing on both (other than Raytheon|Websense):
- Word Attachment, with malicious macro, propagating around the internet this morning... details of the Raytheon|Websense File Sandbox Report found here.
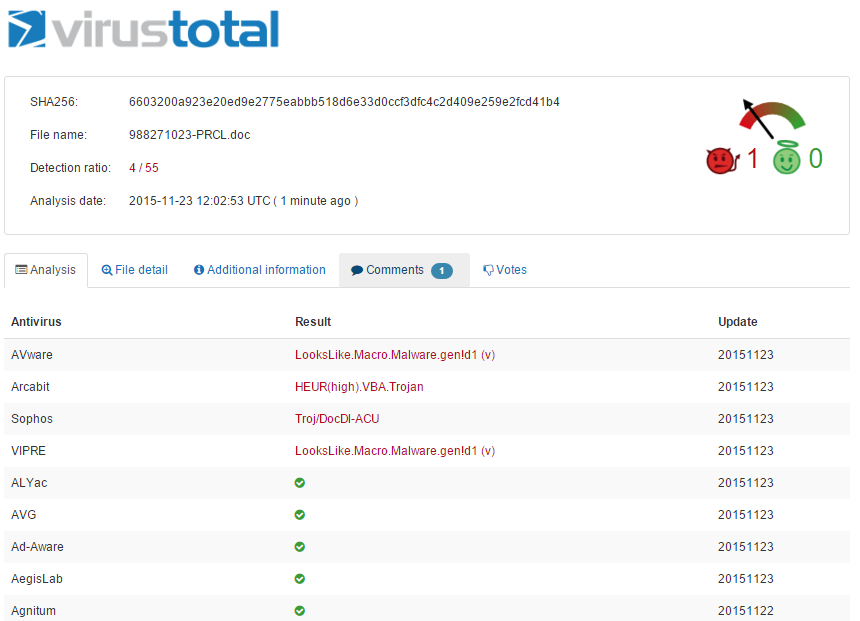
- As is usually the case, your trust would be misplaced if you are expecting your AV engines to block this M$ Office Attachment... as only 4 of 55 AV Companies are detecting this:
- Per the above report, and screen shot below, the downloader phones home to a www site in CZ:
- You are likely asking, "would my web security solution block that outbound connection?" Well... only 1 of 66 Web Security Companies are in fact doing that currently:
In summary, your security solution needs to have a presence in both the email & web security spaces (not to mention identification of proprietary data being ex-filtrated). Call ESPO Systems to learn how this can be done in an effective manner.
Monday, November 16, 2015
Cisco = Detect & Defend?
We see Cisco's new security marketing push; however, that doesn't seem to square with reality currently. Case in point:
- Excel spreadsheet on the loose with a malicious macro. Raytheon|Websense File Sandbox Report here.
- The downloader, per the above report, attempts to pull another exe via HTTP in Finland:
- However, the site in question is currently listed with a "neutral" web reputation. In other words, your users are going there if you are protected by a Cisco IronPort Web Gateway:
In summary, you may ask what the AV Detection Rate for the initial part of the attack (Excel File) is? Not good... only 3 of 54 AV Companies are currently detecting/protecting:
Subscribe to:
Posts (Atom)